SSH-MITM is a man in the middle SSH Server for security audits and malware analysis.
Password and publickey authentication are supported and SSH-MITM is able to detect, if a user is able to login with publickey authentication on the remote server. This allows SSH-MITM to accept the same key as the destination server. If publickey authentication is not possible, the authentication will fall back to password-authentication.
When publickey authentication is possible, a forwarded agent is needed to login to the remote server. In cases, when no agent was forwarded, SSH-MITM can rediredt the session to a honeypot.
Features
- publickey and password authentication
- Phishing FIDO Tokens (Information from OpenSSH)
- hijacking and logging of terminal sessions
- store and replace files during SCP/SFTP file transferes
- port porwarding with SOCKS 4/5 support
- intercept MOSH connections
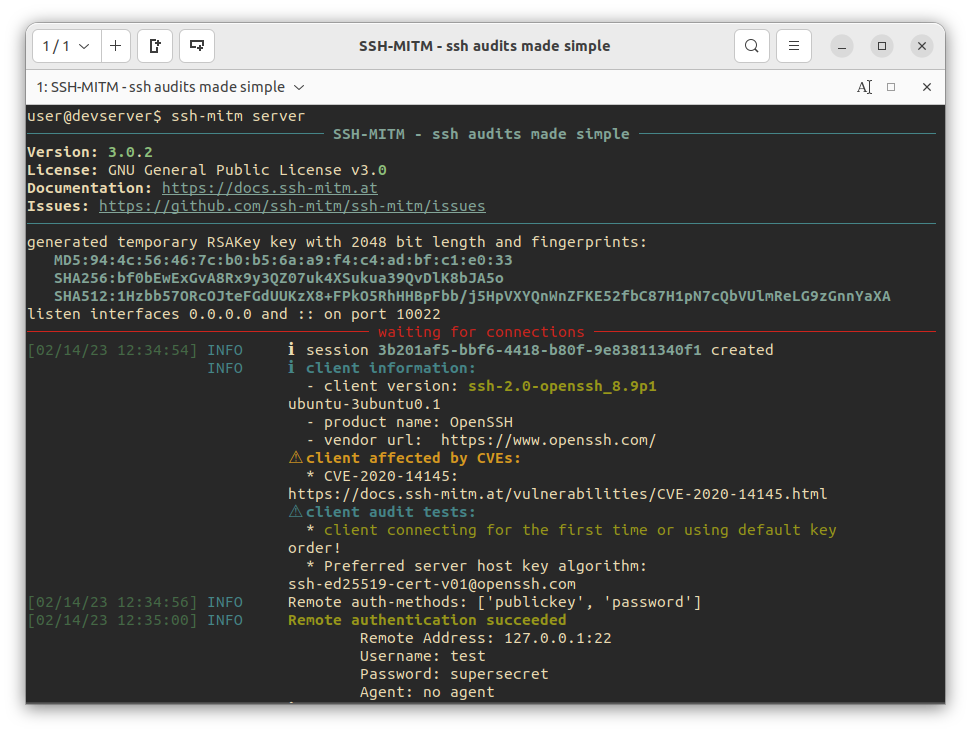
- audit clients against known vulnerabilities
- plugin support
Screenshots
Observed history
| App | Change | Version | When ↑ |
|---|
No observed changes yet.
The initial import establishes a baseline. Future version changes will appear here.
Browse the app catalogue →Upstream releases
Release notes supplied by the developer. These dates are not Flathub package publication times.
6.0.114 Oct 2026
Added
- warn at startup when running as a Flatpak without home/host filesystem access
Changed
- removed the python-json-logger, pytz, colored and psrpcore dependencies
5.0.06 Jul 2024
Changed
- easier plugin development
- merged SOCKS4 and SOCKS5 module in a single module
- prepend entry points with "sshmitm" to avoid name conflicts
- updated vulnerability db