KeyStore Explorer
Multipurpose keystore and certificate tool
org.keystore_explorer.KeyStoreExplorerKeyStore Explorer is an open source, intuitive GUI replacement for the Java command-line utilities keytool and jarsigner.
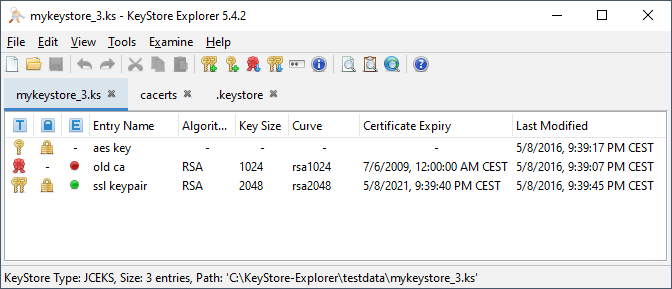
KeyStore Explorer supports creating, managing and examining keystores, keys, certificates, certificate requests, certificate revocation lists and more.
Screenshots
Observed history
| App | Change | Version | When ↓ |
|---|
No observed changes yet.
The initial import establishes a baseline. Future version changes will appear here.
Browse the app catalogue →Upstream releases
Release notes supplied by the developer. These dates are not Flathub package publication times.
v5.6.13 Jan 2026
- Verification of JAR Files
- Post Quantum Cryptography (PQC) Algorithms: ML-DSA, ML-KEM and SLH-DSA
- SM2 and ECGOST
- Improved Key Pair Import
- Store a Password in a KeyStore
- Certificate Validity Information
- Support for Additional Extensions in Certificate Viewer
- Quick Selection of Columns in Main Table
- Export Main Table as CSV
- UI/UX Enhancements, Other Enhancements and Bugfixes
- Support
- Support
- Support
5.6.017 May 2025
- KeyStore Password Manager
- Key Export in JWK Format
- Verification of JWT Signatures
- File signing and verification using PKCS#7/CMS
- Native File Chooser
- New PKCS#12 Features
- New Configuration System
5.5.328 Dec 2023
- Comparing certificates - two ways to compare certificates have been added:
- (1) Comparing certificates: Side-by-side textual comparison: By selecting two certificates in the main view and choosing "Compare" in the context menu, a summary of the most important certificate data and an ASN.1 dump of both certificates is displayed side by side and the differences are marked in a contrasting color (contributed by Jairo Graterón).
- (2) Multiple certificate view dialogs: The certificate viewer dialog is now non-modal, which means several instances of this dialog can be kept open at the same time. This allows to view multiple certificates at the same time (contributed by Piotr Kubiak).
- Added new configuration options:
- (1) Size of generated certificate serial number (contributed by dedabob)
- (2) FlatLaf macOS themes
- Added functionality to examine JWT in system clipboard (contributed by Afonso Fernandes)
- Added PBES2 algorithms as encryption options for PKCS#8 export of private keys:
- (1) PBES2 with SHA-1 and TDES
- (2) PBES2 with SHA-1 and AES-128
- (3) PBES2 with SHA-1 and AES-256
- (4) PBES2 with SHA-256 and AES-256
- Added export button in private key view dialog (contributed by Jairo Graterón)
- Added verify button in the CSR view dialog to check its signature
- Added start of certificate validity as additional optional column for main table view (contributed by Björn Michael)
- Improved certificate key usage and EKU dialogs by adding tooltips with additional details (contributed by The-Lum):
- (1) For the key usage extension the number of the bit (for example 0 for digitalSignature)
- (2) For extended key usage the OID of the key usage
- Enlarged default size of ASN.1 dump window, hex dumps are now displayed in two columns of 8 bytes instead of one (contributed by The-Lum)
- Added total number of revoked certs to CRL view
- Added length info to OCTETSTRING and BITSTRING in ASN1 viewer
- HTTP redirects for downloads of CRLs and CRTs are now supported (contributed by Jairo Graterón)
- Made several adjustments to file extensions used as filters in file chooser dialogs and as default extensions for export files. The reasons were to adapt to existing official standards and also to avoid conflicts with other file types (thanks to Sergey Ponomarev for his investigations):
- (1) Changed default file extension for private key export as DER-encoded PKCS#8 from ".pkcs8" to ".p8" as this extension was registered with IANA (contributed by Sergey Ponomarev)
- (2) Changed default file extension for private key export as DER-encoded PKCS#1/ECPrivateKey from ".key" to ".privkey" (".key" is used for PGP/GPG files and also for Keynote presentations and there seems to be no "official" file extension for these formats)
- (3) Changed default file extension for public key export as DER-encoded RFC 5280 SubjectPublicKeyInfo from ".pub" to ".pubkey" (".pub" is used for MS Publisher files)
- (4) Changed default file extension for PEM-encoded files to ".pem" (usually in combination with a prefix for the actual content like ".p8.pem" or ".pubkey.pem)"
- (5) Added ".p8", ".p8e" and ".pk8" as file extension filters for selecting / importing PKCS#8 files (contributed by Sergey Ponomarev)
- (6) Added ".pem" as file extension filter to all file chooser dialogs that could possibly open PEM files
- Changed dialogs for key pair generation and signing CSRs to display serial number as hex string
- Improved certificate chain detection
- Adjusted password quality meter to show more realistic results
- Replaced IdenTrust's TSA with QuoVadis'
- Improved handling of invalid PEM files
- The certificates selection dialog is now resizable
- Fixed typo in tooltips for public key fingerprint
- Improved French translation (by The-Lum)
- Improved German translation
- Updated third-party libraries to latest versions, BC is now at version 1.77